
Requirements
VertexAI API Permissions
- Go to Cloud VertexAI Library enable API
- Select the
GCP Project ID. - Click on
Enable APIwhich will enable the data catalog api on the respective project.
GCP Permissions
To execute metadata extraction workflow successfully the user or the service account should have enough access to fetch required data. Following table describes the minimum required permissionsMetadata Ingestion
1
Connection Details
Connection Options
GCP Credentials: You can authenticate with your VertexAI instance using eitherGCP Credentials Path where you can specify the file path of the service account key or you can pass the values directly by choosing the GCP Credentials Values from the service account key file.
You can checkout this documentation on how to create the service account keys and download it.
GCP Credentials Values: Passing the raw credential values provided by VertexAI. This requires us to provide the following information, all provided by VertexAI:- Credentials type: Credentials Type is the type of the account, for a service account the value of this field is
service_account. To fetch this key, look for the value associated with thetypekey in the service account key file. - Project ID: A project ID is a unique string used to differentiate your project from all others in Google Cloud. To fetch this key, look for the value associated with the
project_idkey in the service account key file. You can also pass multiple project id to ingest metadata from different VertexAI projects into one service. - Private Key ID: This is a unique identifier for the private key associated with the service account. To fetch this key, look for the value associated with the
private_key_idkey in the service account file. - Private Key: This is the private key associated with the service account that is used to authenticate and authorize access to VertexAI. To fetch this key, look for the value associated with the
private_keykey in the service account file. - Client Email: This is the email address associated with the service account. To fetch this key, look for the value associated with the
client_emailkey in the service account key file. - Client ID: This is a unique identifier for the service account. To fetch this key, look for the value associated with the
client_idkey in the service account key file. - Auth URI: This is the URI for the authorization server. To fetch this key, look for the value associated with the
auth_urikey in the service account key file. The default value to Auth URI is https://accounts.google.com/o/oauth2/auth. - Token URI: The Google Cloud Token URI is a specific endpoint used to obtain an OAuth 2.0 access token from the Google Cloud IAM service. This token allows you to authenticate and access various Google Cloud resources and APIs that require authorization. To fetch this key, look for the value associated with the
token_urikey in the service account credentials file. Default Value to Token URI ishttps://oauth2.googleapis.com/token. - Authentication Provider X509 Certificate URL: This is the URL of the certificate that verifies the authenticity of the authorization server. To fetch this key, look for the value associated with the
auth_provider_x509_cert_urlkey in the service account key file. The Default value for Auth Provider X509Cert URL ishttps://www.googleapis.com/oauth2/v1/certs - Client X509Cert URL: This is the URL of the certificate that verifies the authenticity of the service account. To fetch this key, look for the value associated with the
client_x509_cert_urlkey in the service account key file. GCP Credentials Path: Passing a local file path that contains the credentials. Location: Location refers to the geographical region where your resources, such as datasets, models, and endpoints, are physically hosted.(e.g.us-central1,europe-west4)
2
Test the Connection
Once the credentials have been added, click on Test Connection and Save the changes.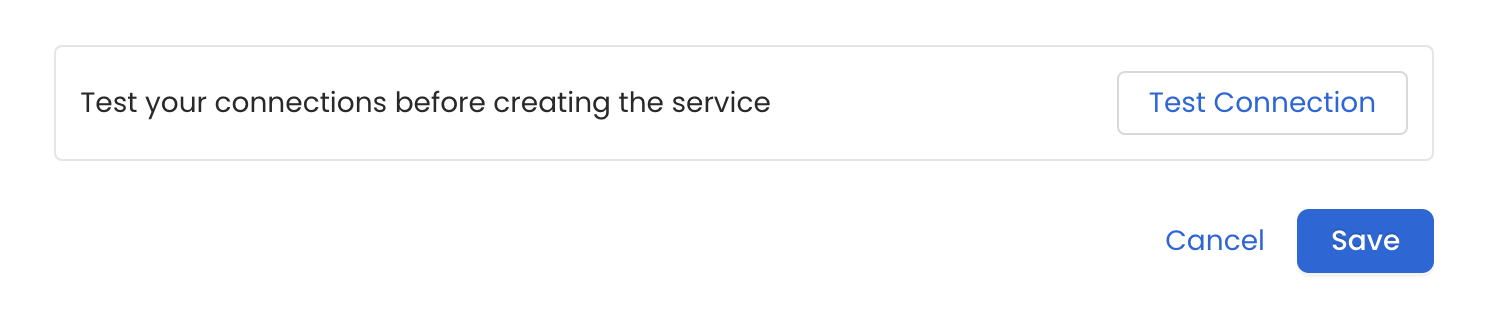
3
7. Configure Metadata Ingestion
In this step we will configure the metadata ingestion pipeline,
Please follow the instructions below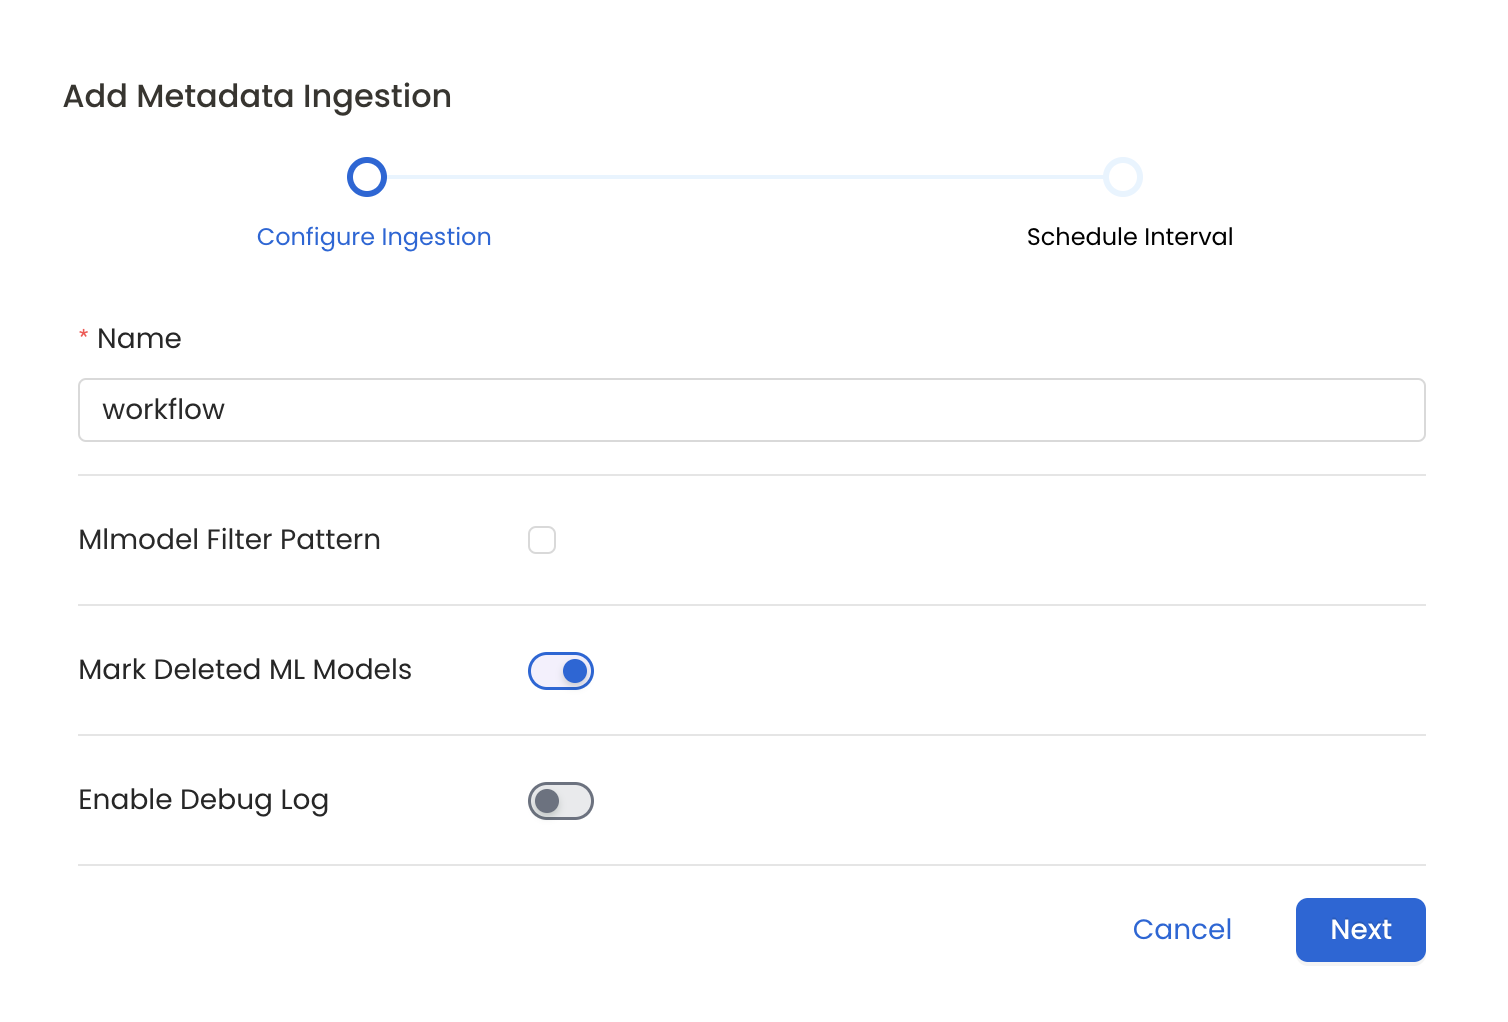
Metadata Ingestion Options
- Name: This field refers to the name of ingestion pipeline, you can customize the name or use the generated name.
- Mark Deleted Ml Models (toggle):: Set the Mark Deleted Ml Models toggle to flag ml models as soft-deleted if they are not present anymore in the source system.
- ML Model Filter Pattern (Optional): To control whether to include an ML Model as part of metadata ingestion.
- Include: Explicitly include ML Models by adding a list of comma-separated regular expressions to the Include field. OpenMetadata will include all ML Models with names matching one or more of the supplied regular expressions. All other ML Models will be excluded.
- Exclude: Explicitly exclude ML Models by adding a list of comma-separated regular expressions to the Exclude field. OpenMetadata will exclude all ML Models with names matching one or more of the supplied regular expressions. All other ML Models will be included.
- Enable Debug Log (toggle): Set the Enable Debug Log toggle to set the default log level to debug.
4
Schedule the Ingestion and Deploy
Scheduling can be set up at an hourly, daily, weekly, or manual cadence. The
timezone is in UTC. Select a Start Date to schedule for ingestion. It is
optional to add an End Date.Review your configuration settings. If they match what you intended,
click Deploy to create the service and schedule metadata ingestion.If something doesn’t look right, click the Back button to return to the
appropriate step and change the settings as needed.After configuring the workflow, you can click on Deploy to create the
pipeline.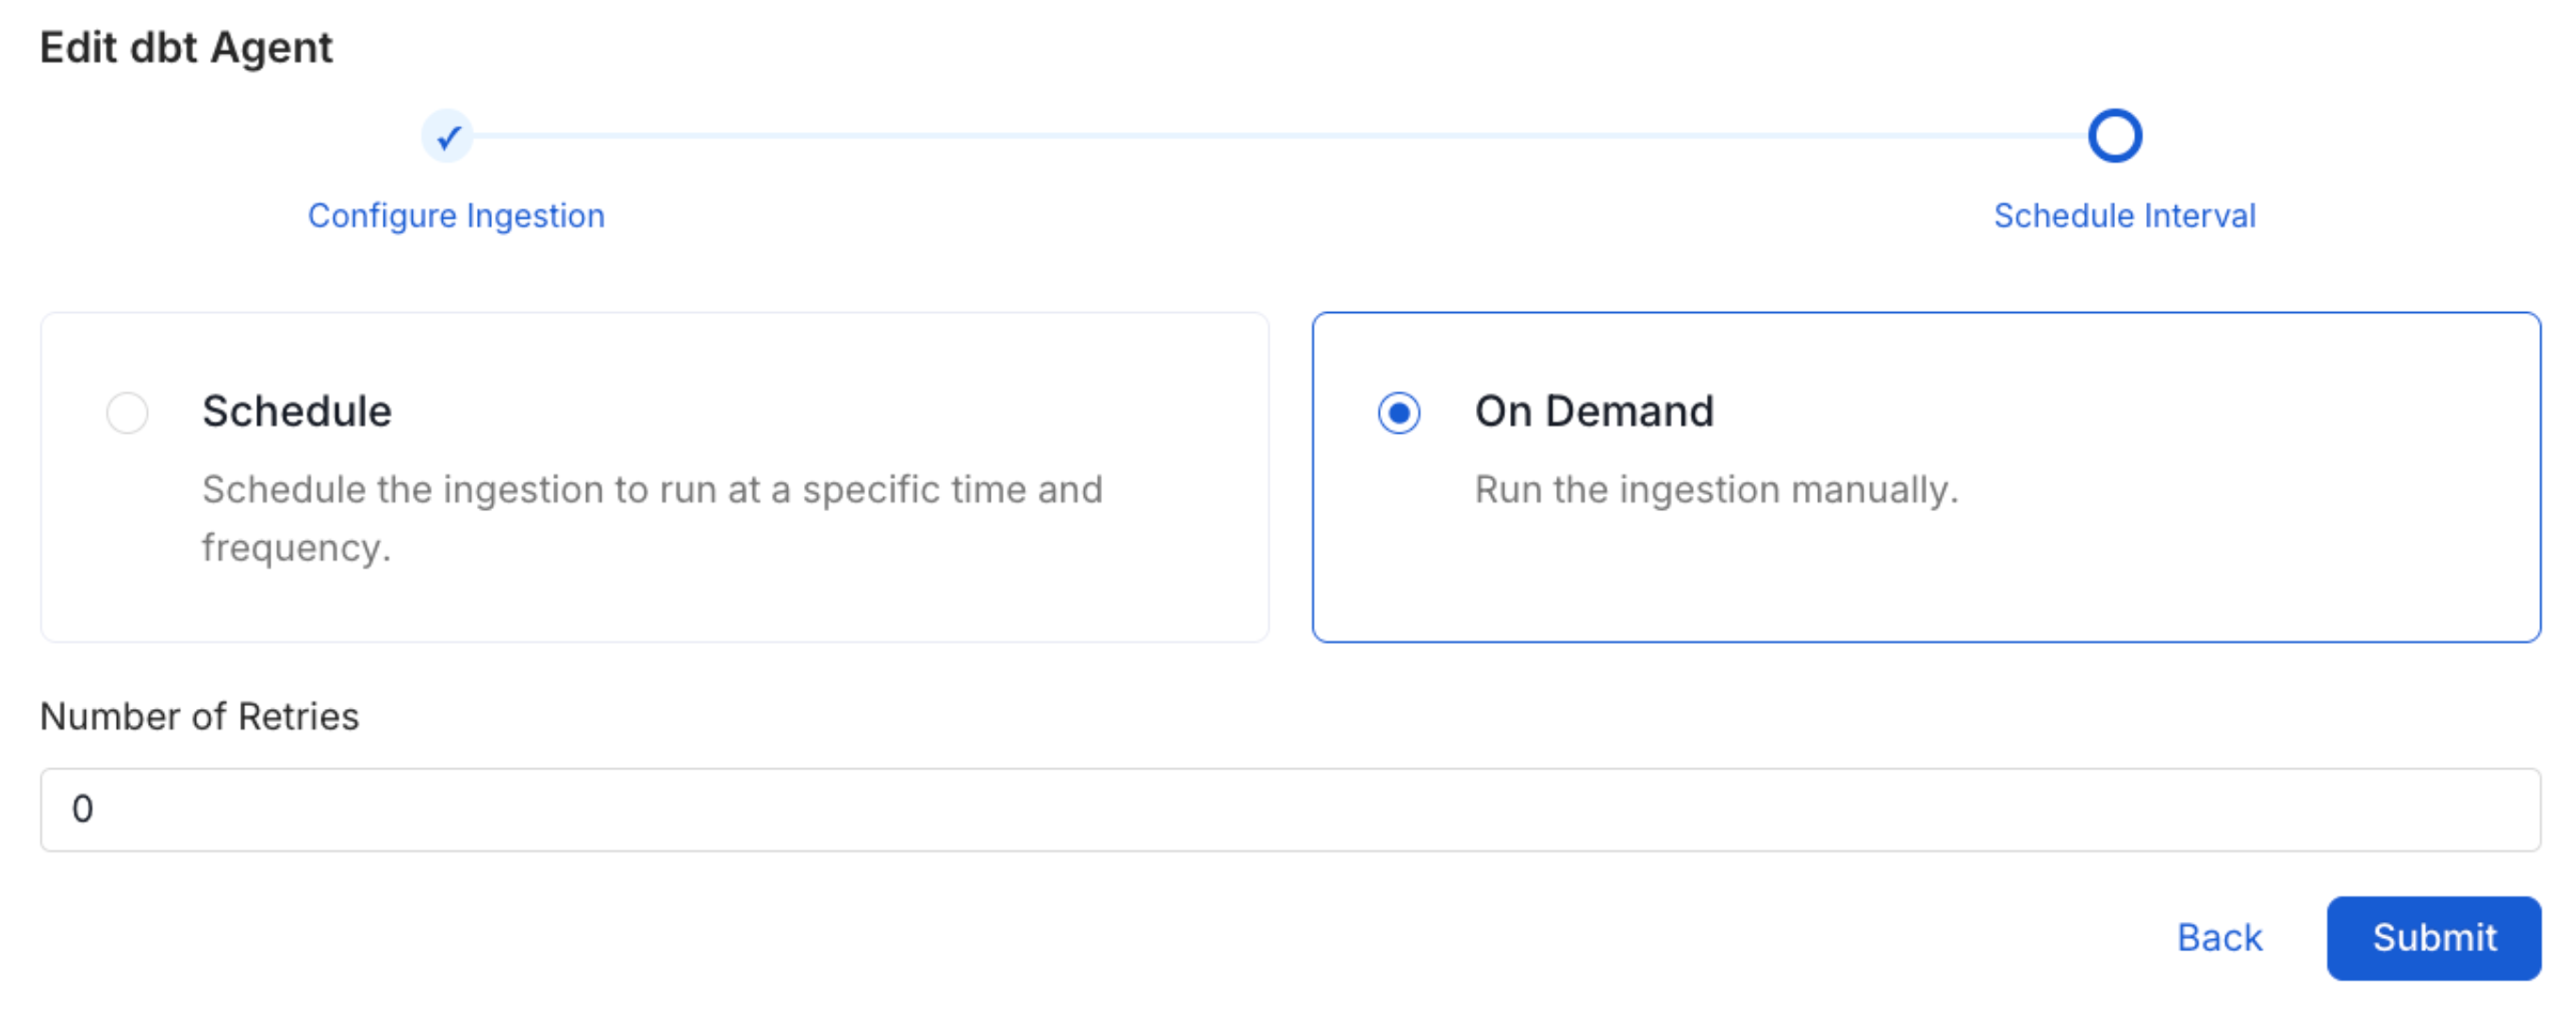
5
View the Ingestion Pipeline
Once the workflow has been successfully deployed, you can view the
Ingestion Pipeline running from the Service Page.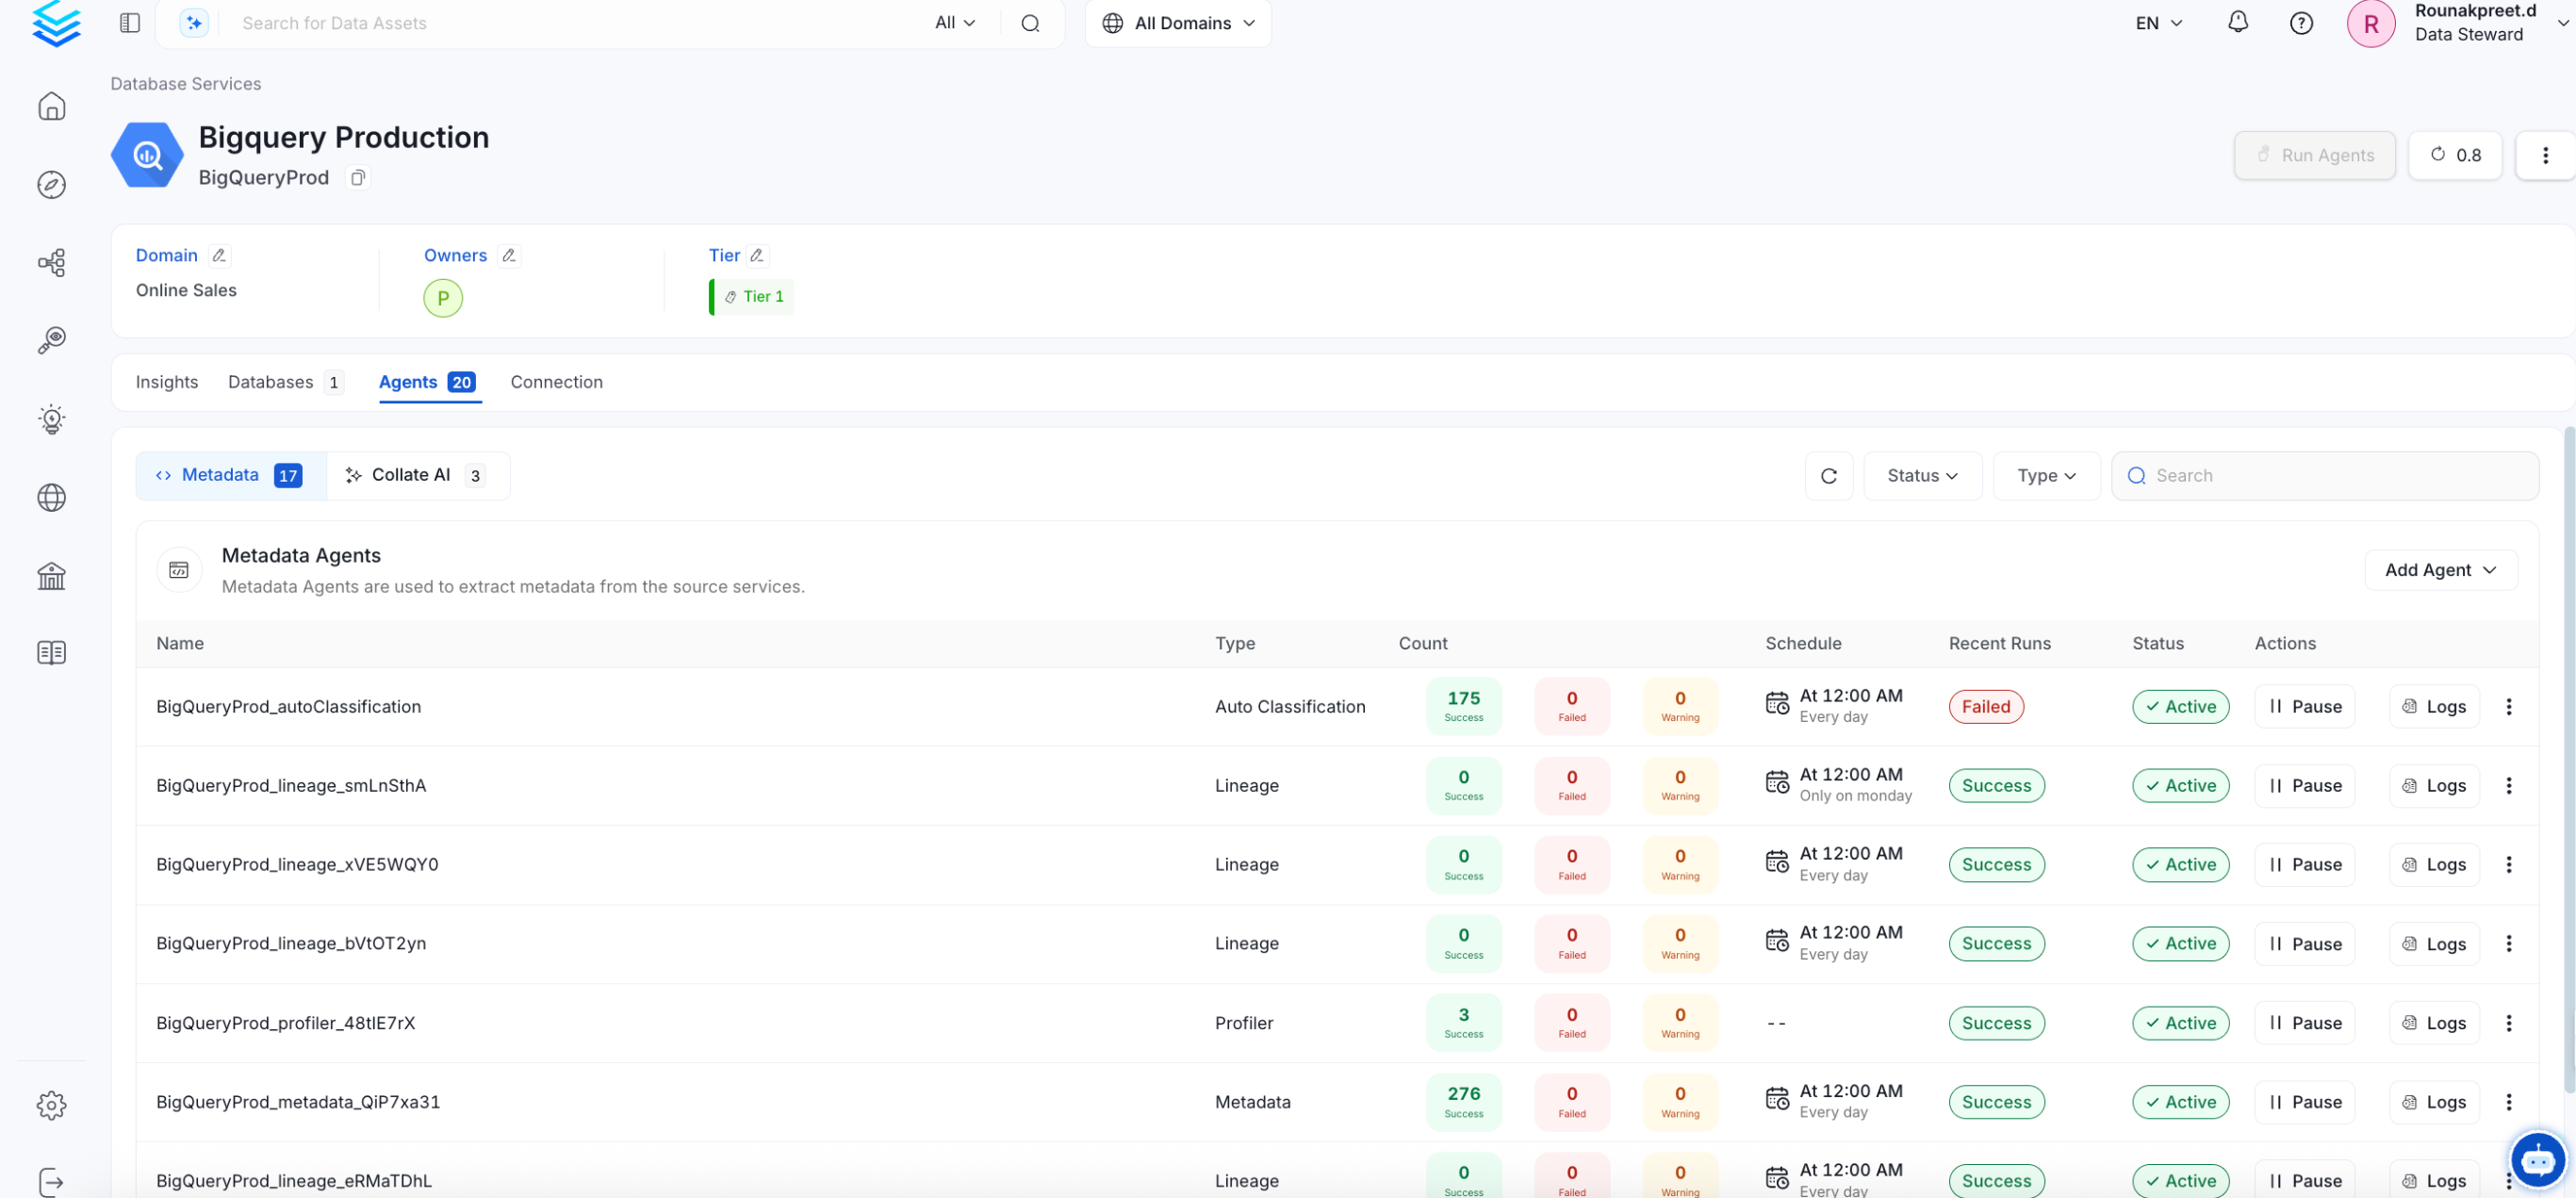
Troubleshooting
VertexAI Troubleshooting
Learn more about how to troubleshoot common VertexAI connector issues and resolve configuration or ingestion errors.